
Abonnieren Sie unseren neuen Newsletter für Zertifizierungsstellen-Profis & ISO-Auditoren → Hier
The transition period for ISO/IEC 17020:2026 is already running, and some accreditation bodies like DAkkS accepts transition applications from 1 November 2026. TIC OS gives certification and inspection bodies one place for procedures, competence records, audit planning and assessment ready evidence, from application to certificate.
The 2012 editions of the conformity assessment standards are being replaced one by one. These dates are confirmed by ISO, DAkkS and UKAS:
ISO/IEC 17065: DAkkS will publish transition guidance once the German version of the revised standard is published by DIN.
A new standard edition is more than a document update. Your accreditation body expects you to show that the changes are understood, implemented and working before the transition assessment. DAkkS asks inspection bodies to document their transition arrangements and a transition plan, and UKAS asks for a gap analysis proforma at least one month before the assessment. In practice, most bodies will work through the same steps:
Compare the new edition with your current management system and decide what needs to change.
Update the manual, procedures, checklists, report and certificate templates, and contract documents. Keep meeting the old edition until your new accreditation is granted.
Show how you identify and monitor risks to impartiality, and how you make sure competent personnel are available, including external auditors and inspectors.
Be ready to explain how you control data and information, how you validate and secure the software you use, and how you oversee any AI.
Prepare traceable records that assessors can sample without days of document chasing.
Make sure staff affected by the changes understand the revised requirements.
UKAS highlights among other things: the independence types are simplified to Type A and Type non A, impartiality requirements are strengthened, a new section covers data and information control (including software validation and security), controls on externally provided services are broadened (including provider registers), and risk and opportunity management replaces preventive action.
ISO/IEC 17024:2026 goes further on AI. According to UKAS, it requires certification bodies to validate, oversee and disclose their use of AI, with human oversight of AI outcomes. This is a clear signal of what accreditation bodies will ask about the tools you use.
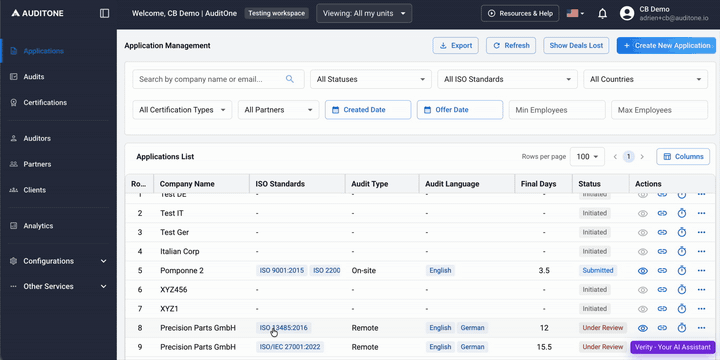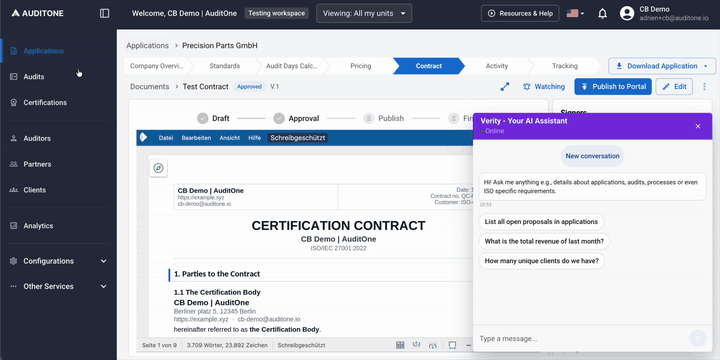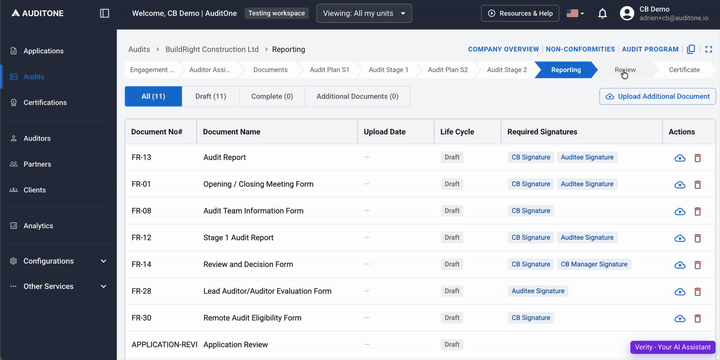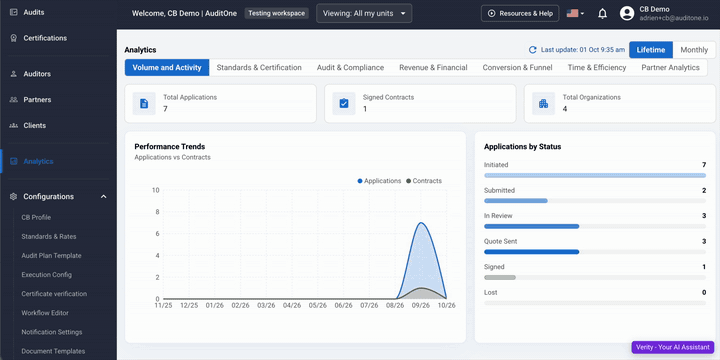
TIC OS is AuditOne's AI native operating system for certification and inspection bodies. It covers ISO/IEC 17021, 17020 and 17065 service types in one platform, from application and contract review through planning, scheduling, fieldwork and reporting to the certification decision and certificate issuance.
Daten werden bei der Übertragung und im Ruhezustand nach branchenüblichen Protokollen verschlüsselt
Rollenbasierte Zugriffskontrolle (RBAC) und granulare Berechtigungen
Umfassende Audit-Protokolle und Exportfunktionen für die Aufsicht
EU-Datenresidenzoptionen für Compliance-Anforderungen verfügbar
Aktives Schwachstellen-Meldeprogramm und Sicherheitstests
Funktionen, die auf ISO/IEC 27001 und Datenschutzpraktiken abgestimmt sind
Transformieren Sie Ihre Audit-Abläufe mit intelligenter Automatisierung und Zugang zum Auditoren-Netzwerk.

Ausgereifte Algorithmen & Automatisierungen ermöglichen es Ihrem Team, sich auf fachliche Beurteilung statt Copy-Paste zu konzentrieren. Bewahren Sie Audit-Exzellenz und eliminieren Sie gleichzeitig repetitive Aufgaben.

Planen Sie mit Ihrem eigenen Team oder nutzen Sie bei Bedarf an Nischenexpertise Europas größtes ISO/SEC-Auditorennetzwerk. Skalieren Sie nach Bedarf, ohne Kompromisse bei der Qualität.

Vorprüfung von Dokumenten, Besprechungstranskripte, vorgeschlagene Fragen und Nachweiserfassung – stets mit Mensch im Kontrollprozess. KI, die die fachliche Beurteilung erweitert, niemals ersetzt.


When do I have to transition to ISO/IEC 17020:2026?

TIC OS ist eine End-to-End-Softwarelösung für Zertifizierungsstellen (CBs) zur Verwaltung von Audits, Kunden-Onboarding, Planung & Terminierung, Auditorenzuweisung, Nachweiserfassung, Berichterstattung, Zertifikatsausstellung und Abrechnung – mit optionaler KI-Unterstützung. Der gesamte Zertifizierungszyklus wird mit optimierten Prozessen und effizienter Kommunikation abgedeckt.
Has ISO/IEC 17065 been revised?
Akkreditierte und nicht akkreditierte Zertifizierungsstellen, Konformitätsbewertungsstellen und größere interne Audit-Teams, die ISO-Schemata (z. B. ISO 9001, ISO 14001, ISO/IEC 27001) oder ähnliche Rahmenwerke anwenden.
What does ISO/IEC 17024:2026 require on AI?
Im Standardsetup unterstützt: ISO 9001, ISO 14001, ISO 22000, ISO 22301, ISO/IEC 27001, ISO 37001, ISO/IEC 42001, ISO 45001, ISO 50001
Optional: SOC 2, NIST, NDIS, IFS & weitere
Individuelle Vorlagen können ergänzt werden, um weitere Standards und Dienstleistungen abzudecken. Die CRM- und Business-Intelligence-Funktionen funktionieren über alle Rahmenwerke hinweg.
How should a certification or inspection body prepare for the transition assessment?
Es gibt zwei Teile:
1) Der Stage-1-Audit-Agent prüft hochgeladene Dokumente vorab und markiert Lücken.
2) Der Meeting-Assistent (optional) transkribiert Calls, versieht Nachweise mit Zeitstempeln und schlägt Folgeaktionen vor. Alle Ausgaben sind editierbar; Auditoren behalten stets die Kontrolle.
Does TIC OS make my body compliant with the new standards?
Die Tarife sind nach Kundenanzahl gestaffelt oder als vereinbarter Festpreis verfügbar. Kontaktieren Sie uns für weitere Informationen und eine Demo.
Can TIC OS support an ISO/IEC 42001 scope extension?
Nachweise sind mit vollständigen Audit-Trails an Feststellungen und Klauseln geknüpft. Aufbewahrungsfristen sind je nach Schema oder Kundenrichtlinie konfigurierbar.
See how TIC OS supports ISO/IEC 17021, 17020 and 17065 workflows, from application to certificate, with records your assessor can follow.


